Capabilities

Regulatory Compliance Strategy & Documentation

    Navigate the regulatory landscape with confidence. We align your organization with NERC CIP and NIST frameworks by translating requirements into clear, actionable controls. Whether you need a program build, a documentation review, or audit preparation, we ensure your security posture meets rigorous industry expectations.

Risk & Threat Assessments

    We conduct comprehensive assessments across IT, OT, and building systems by integrating threat intelligence with attack surface mapping. Our approach uncovers systemic vulnerabilities, including supply chain risks and cascading impacts, to deliver actionable insights for technical remediation, architecture hardening, and incident response.

Explore Insights from our Team of Experts

Architecture Reviews

    Ensure your architecture is defensible and compliant. We analyze your converged environments to identify gaps in segmentation, identity, and trust zones. You receive actionable strategies to harden your defenses against advanced threats without compromising operational performance.

Policy & Governance Development

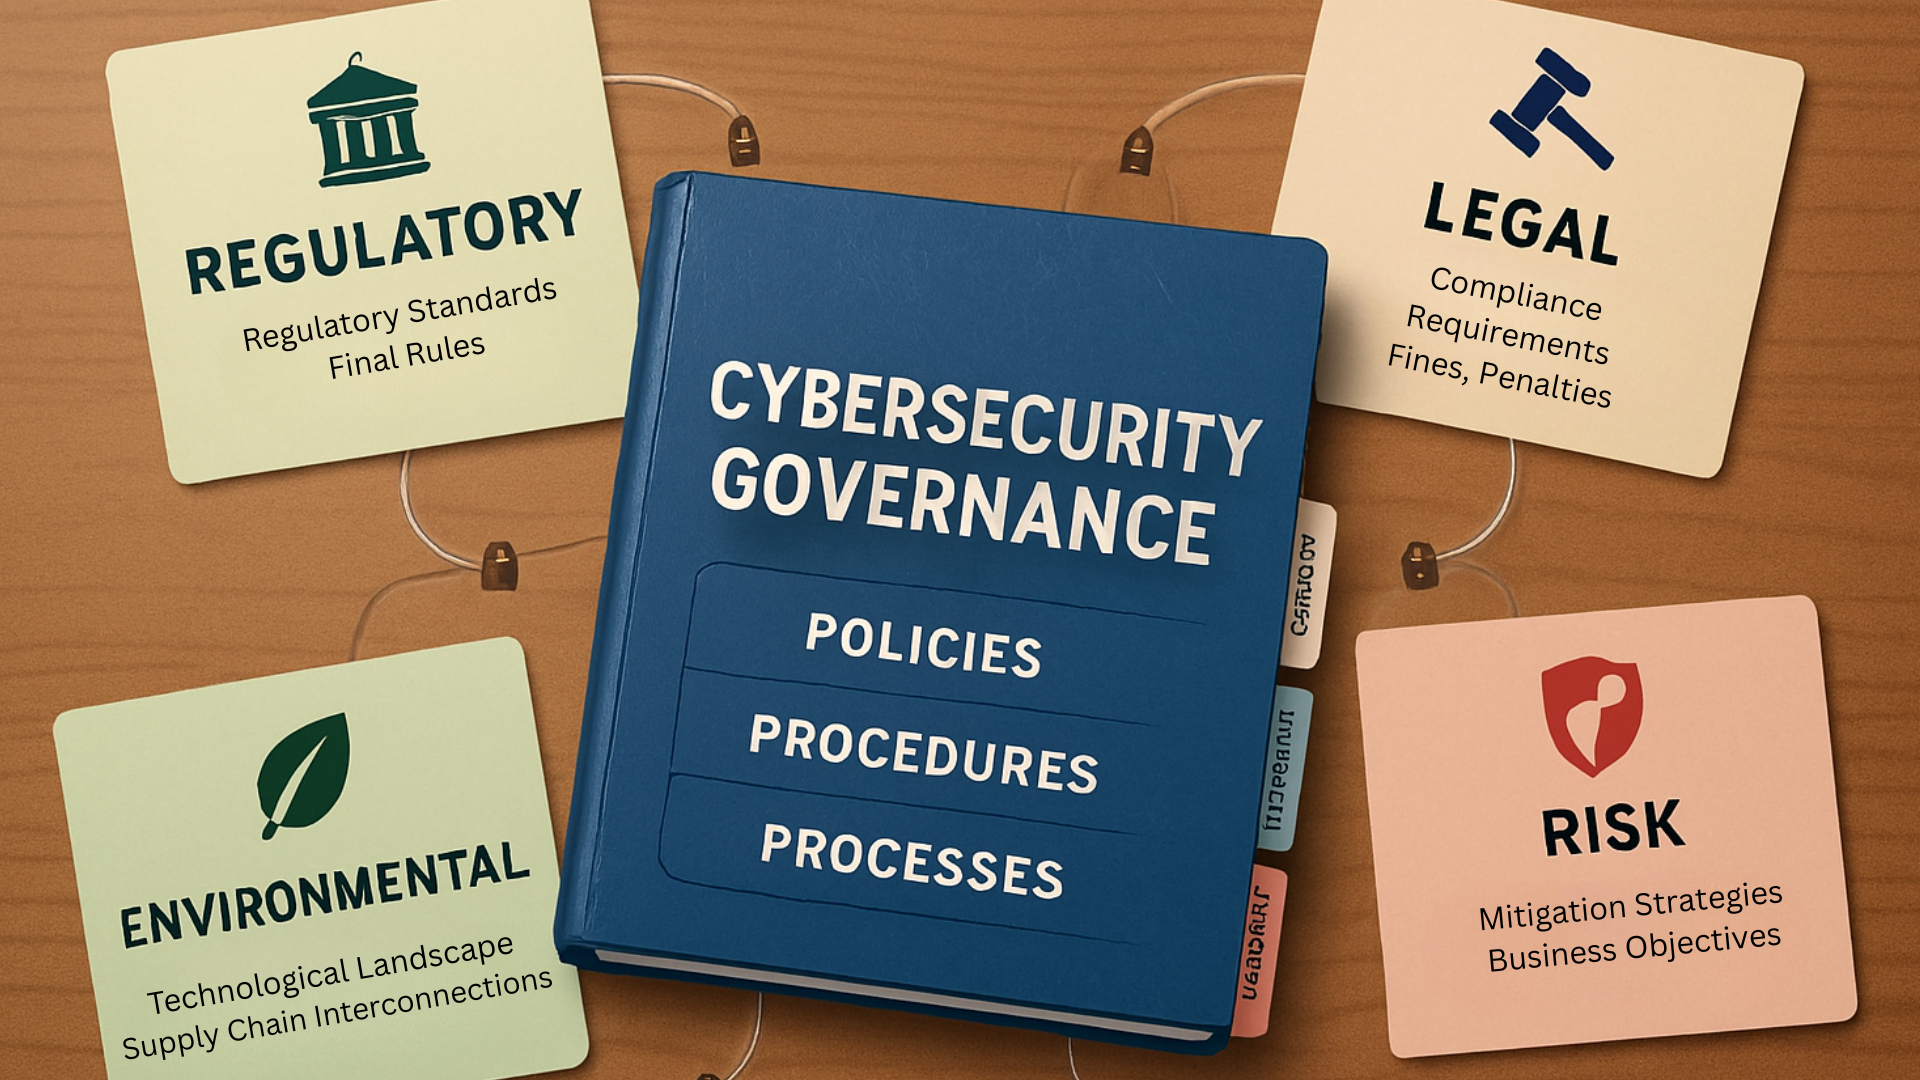
    Transform compliance into culture with governance structures that support true accountability. We bridge the gap between regulatory requirements and daily operations by delivering clear, defensible policies and procedures that ensure sustainable risk management.

Cybersecurity Workshops, Seminars, & Training

    Empower your workforce with training grounded in technical rigor and industry standards. Whether for technical staff or leadership, our scenario-based learning drives a culture of security, ensuring your team is prepared to defend against advanced threats and navigate regulatory pressures.